Third party compliance gaps become your regulatory exposure
Compliance risk doesn’t just originate inside your organization; it often begins with third parties. You can have strong policies, controls, and compliance programs inside your own organization and still be held accountable when something goes wrong with a vendor.
Supply Wisdom helps compliance teams spot these developments across their vendor network and quickly understand which ones may require a closer look, before they turn into a larger regulatory or business issue.
Without continuous monitoring:

Changes in a third party’s compliance posture go unnoticed between periodic reviews

Your teams can’t tell which developments warrant investigation versus continued monitoring

Investigation starts after the issue has already escalated

A single compliance event gets treated as the whole problem instead of a sign of broader exposure
Supply Wisdom helps organizations continuously monitor third-party risk in support of key regulatory, compliance, and supervisory frameworks, including:
What Supply Wisdom helps you do
Know when a third party’s compliance status changes
Track regulatory investigations, enforcement actions, sanctions, fraud allegations, lawsuits, fines, license revocations, and other developments that could change a third-party’s risk profile.
Extend due diligence beyond onboarding
Keep monitoring third parties after initial due diligence is complete, so compliance concerns are identified in between periodic reviews.
Uncover compliance exposure across your third-party network
See whether an issue is isolated to one third party or extends across related entities, locations, fourth parties, and other critical dependencies.

Prioritize the compliance risks that require action
Set alerts based on third-party criticality, risk type, geography, and other criteria so your team can focus on events that warrant investigation, escalation, or remediation.

Investigate issues with the context you need
Get analyst-reviewed intelligence on what happened, who is involved, the severity and potential impact, and the context your team needs to determine the appropriate response.

Understand the broader impact of a compliance event
See when sanctions, enforcement actions, fraud, misconduct, or other compliance issues create additional risk.
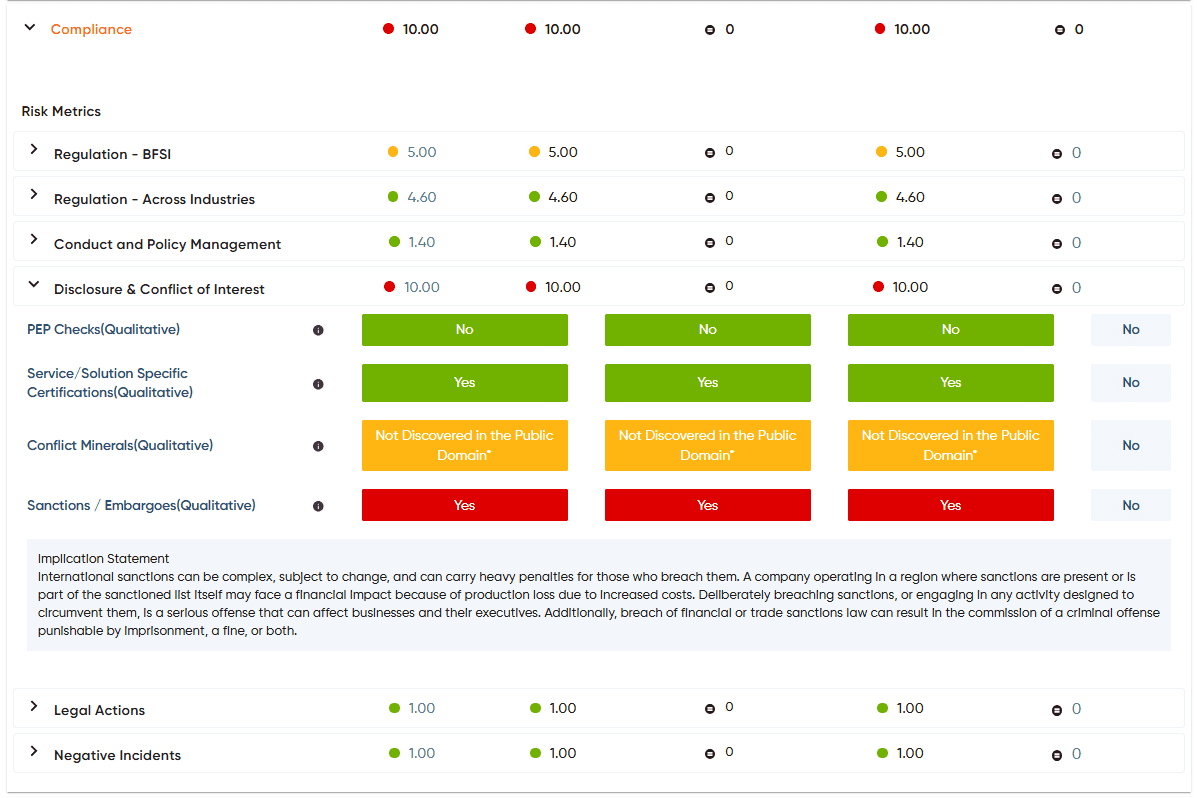
Capture everything. Surface what matters most. These are examples of the event types we can monitor in this domain. You decide which signals matter, which vendors or groups they apply to, and what should trigger an alert.
1
Regulatory risk
Regulatory probes and investigations
Enforcement actions
New regulatory requirements
Statutory compliance obligations
2
Governance and market confidence
Credit actions
Insider selling
Regulatory enforcement
Fraud-related developments
3
Legal disputes & penalties
Lawsuits and court rulings
Settlements
Fines and penalties
Liens and license revocations
4
Capital and liquidity events
Debt activity
Funding withdrawal
Buybacks
IPO-related signals
5
Compliance violations & operational restrictions
Compliance violations
Regulatory restrictions
Licensing issues
Other events that could affect a third party’s ability to operate